The App Hosting Trap: Why Enterprises Build Private Clouds
Renting infrastructure vs. Owning your architecture.
Public Platform-as-a-Service (PaaS) providers offer rapid prototyping, but they punish you for success. As your SaaS scales, you are hit with runaway egress data fees, restrictive API limits, and "noisy neighbor" CPU throttling. Migrating your application hosting to a paas private architecture is the only way to reclaim performance and budget predictability.
Database I/O Contention in Kubernetes
Many organizations force heavy stateful databases into Kubernetes clusters. While modern K8s StatefulSets prevent data corruption, running high-traffic databases alongside containerized microservices creates severe I/O contention and memory caching limits. iRexta isolates your workloads: K8s for stateless microservices, and dedicated Bare Metal (Shared-Nothing Architecture) for databases to guarantee 100% dedicated NVMe IOPS and unthrottled memory allocation.
The "Downtime During Updates" Flaw
Restarting services drops active user sessions. True enterprise architecture demands zero downtime microservices. We engineer load-balanced delivery pipelines that shift traffic seamlessly, ensuring you never take your application offline to push a patch.
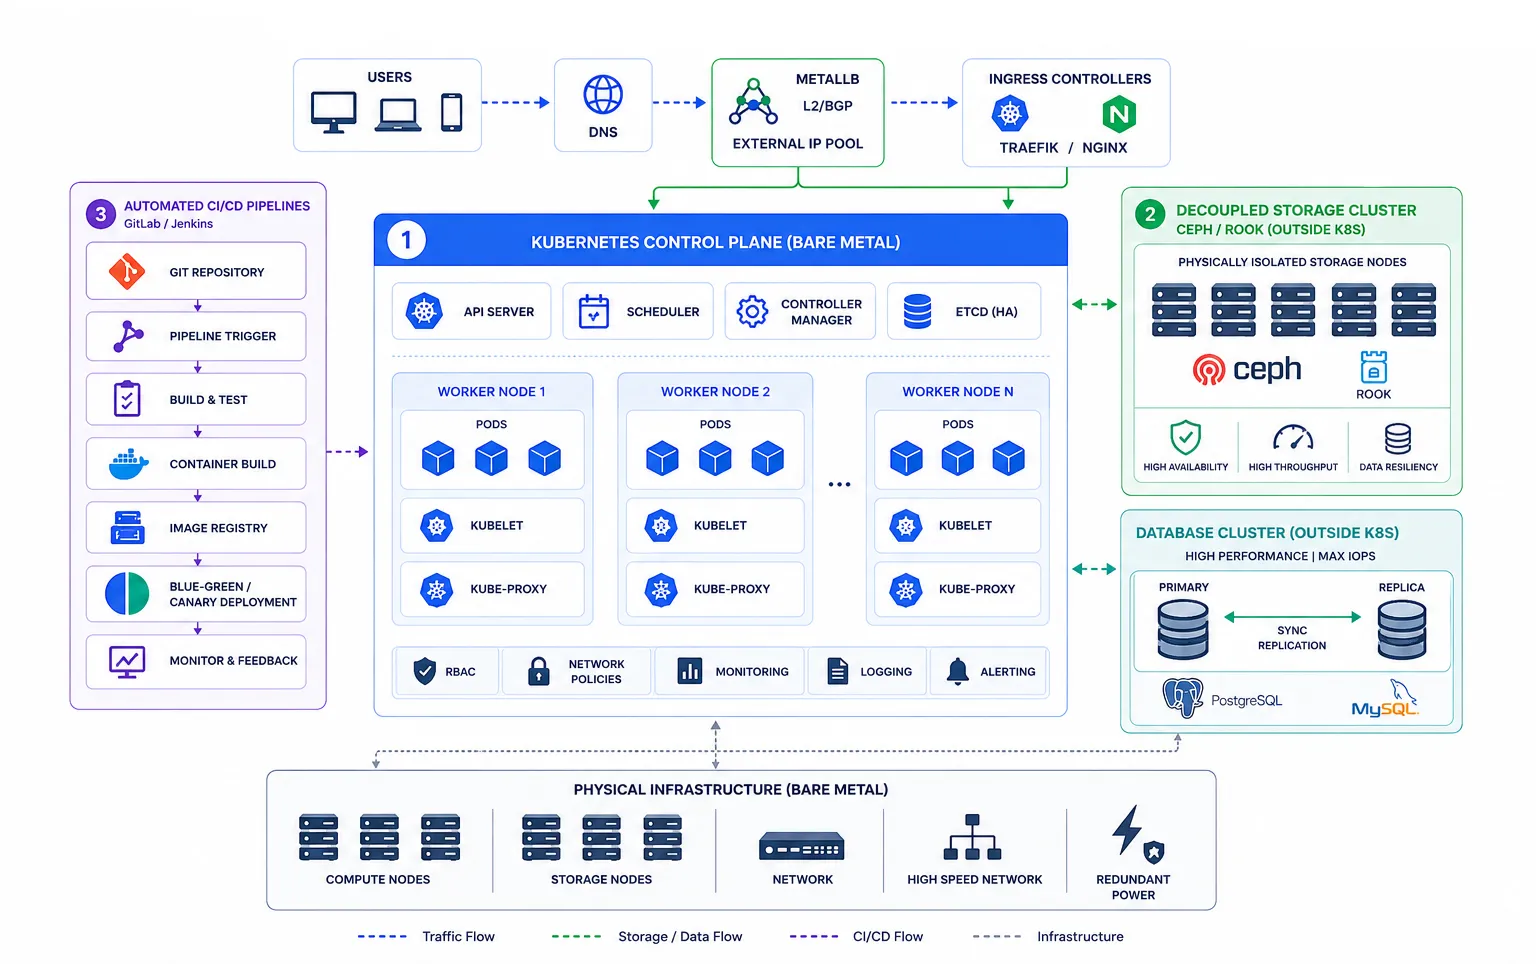
Enterprise Application Architecture Blueprint
How do you transition from an expensive public cloud to an enterprise-grade highly available infrastructure? Upon request, iRexta's SRE team will architect this exact blueprint on your bare metal servers:
- 1. The Kubernetes Control Plane: We deploy a managed kubernetes cluster directly on bare metal. To overcome bare metal routing limitations, we configure MetalLB to dynamically assign external IPs to your ingress controllers (Traefik/NGINX), replicating cloud-native load balancing.
- 2. Decoupled Storage & Database Clusters: We architect PostgreSQL/MySQL outside of K8s for maximum IOPS. For persistent container volumes (CSI), we integrate Ceph/Rook on physically isolated Storage Nodes, ensuring the "Ceph CPU Tax" never steals compute power from your API microservices.
- 3. Automated CI/CD Pipelines: We implement a managed ci/cd deployment infrastructure (GitLab/Jenkins) that integrates with your Git repository, automating testing, container builds, and progressive Blue-Green rollouts.
Enterprise Workloads. Total Isolation.
Build robust enterprise application hosting architecture designed to scale horizontally. Whether you are running a B2B SaaS or a high-traffic E-commerce platform, we provide the ultimate foundation.
SaaS High Availability
High availability is sustained operationally, not just architecturally. We eliminate the Single Point of Failure (SPOF) at the edge by deploying clustered HAProxy nodes backed by Keepalived (VRRP). This external layer securely filters and routes traffic into your internal Kubernetes MetalLB environment, ensuring seamless failovers and achieving true high availability (99.99% uptime) for your critical B2B applications.
Seamless CI/CD Deployments
Deploy multiple times a day without fear. We engineer Blue-Green and Canary deployment pipelines. Your new code is verified in production with a fraction of live traffic before seamlessly taking over, ensuring zero disruption to active user sessions.
High-Traffic Database Clusters
Don't let your database become the bottleneck. We design robust managed db solutions (PostgreSQL, MySQL, MongoDB) using Master-Replica architectures over a private VLAN, ensuring immediate failovers and unthrottled read/write query speeds.
Mandatory Security & Operational Rules
Enterprise infrastructure requires strict governance. iRexta enforces these critical SRE security protocols to protect your application layer.
Security Warning: API Exposure
Never expose your internal microservices directly to the web. iRexta mandates the deployment of an API Gateway (such as Kong or Traefik) at the edge of your Private VPC. This gateway handles JWT authentication, strict rate-limiting, and SSL termination before traffic ever touches your containerized application layer.
Warning: Database Schema Evolution
Rolling out a Blue-Green deployment can fatally corrupt your database if the schema is out of sync. Our DevOps architecture enforces strict Backward-Compatible Schema Evolution. This ensures that both the old (Blue) and new (Green) versions of your microservices can read and write to the database simultaneously without data loss.
Application Hosting Strategic Showdown
See why forward-thinking enterprises migrate from restrictive Cloud PaaS to an iRexta managed application environment.
| Infrastructure Metric | iRexta Application Hosting (Managed Bare Metal) | Public Cloud PaaS (AWS/Azure) |
|---|---|---|
| Compute Power | 100% Dedicated CPU. Zero Hypervisor Tax. | Shared vCPUs with "Noisy Neighbor" throttling. |
| Network Egress Fees | Flat-Rate Unmetered (10Gbps+). Zero surprise bills. | Pay-per-Gigabyte. Extremely expensive at scale. |
| Architectural Control | Full Root Access. Bring Your Own Middleware. | Vendor Lock-in. Forced to use proprietary APIs. |
| Data Sovereignty | Absolute data isolation via hardware boundaries. | Data resides on multi-tenant shared infrastructure. |
Focus on Your Code. We Manage the Cluster.
Rent the raw bare metal to build your own stack, or request our Managed DevOps team to architect a highly available Private PaaS for your enterprise application. Let's design your blueprint today.